Verizon, one of the largest American telecommunications companies, has disclosed a data breach impacting 63,206 individuals. The inadvertent disclosure of personal data was attributed to employee wrongdoing.
In a data breach notification filed with authorities in the US state of Maine, Verizon disclosed that on around September 21st, 2023, a company employee obtained a file containing certain employees’ personal information without authorization and violating Verizon policy.
According to Verizon’s letter to affected users, the information contained in the file may include name, address, Social Security number or other national identifier, gender, union affiliation, date of birth, and compensation information.
“At this time, we have no evidence that this information has been misused or shared outside of Verizon as a result of this issue. We are working to ensure our technical controls are enhanced to help prevent this type of situation from reoccurring and are notifying applicable regulators about the matter,” the notification reads.
In the filing form, dated February 5th, Verizon describes the leak as “inadvertent disclosure, insider wrongdoing.”
Verizon has arranged complimentary credit monitoring and identity protection services for affected individuals, covering up to $1 million in potential fraud damages for 24 months.
“We encourage you to remain vigilant against incidents of identity theft and fraud by monitoring your free credit reports and reviewing your account statements,” the company said.
More than 117,000 employees worked for Verizon in 2022, according to Statista. The wireless carrier has over 144.8 million subscribers.
Direct Trading Technologies, an international fintech company, jeopardized over 300K traders by leaking their sensitive data and trading activity, thereby putting them at risk of an account takeover.
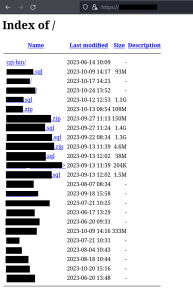
On October 27th, the Cybernews research team discovered a misconfigured web server with backups and development code references allegedly belonging to the fintech company Direct Trading Technologies.
Direct Trading Technologies (DTT) is an international fintech company offering trading platforms for stocks, forex, precious metals, energies, indices, Contracts for Difference (CFDs), and cryptocurrencies. Also, DTT offers white-label services for fintech solutions.
While the main clientele is based in Saudi Arabia, the company has offices in the UK, Lithuania, UAE, Kuwait, Colombia, Turkey, Bahrain, Lebanon, and the Republic of Vanuatu.
The discovered directory included multiple database backups, each holding a significant amount of sensitive information about the company’s users and partners. The leak poses a variety of risks, expanding from identity theft to takeover and cashing-out accounts of traders.
Cybernews contacted the company with our findings. While the problem was fixed, an official response from the company is still yet to be received.
Miracle Software Systems left an unprotected instance, exposing millions of messages between thousands of corporate users, some of which discussed corporate secrets.
Even though official documents are extremely sensitive, corporate chat histories can be just as revealing, especially when millions of messages are involved. Meanwhile, the Cybernews research team has recently discovered an open MongoDB instance with over 11 million Rocket.Chat messages between 3,062 users.
Rocket.Chat is an open-source collaboration platform that uses MongoDB as its default storage database, sometimes leading to data-exposing misconfiguration accidents.
“Based on our analysis, the entire Miracle Software infrastructure, and potentially the assets of their clients, were compromised,” researchers said.
According to the team, the exposed database contained two gigabytes of text messages. Essentially, everything that employees and customers discussed via Miracle’s Rocket.Chat platform was exposed. Only a small data sample revealed that the leak exposed:
Our researchers believe that the MongoDB instance was open for at least three days in the junction between November and December and is no longer publicly available.
Data leaks of this magnitude pose severe risks to companies, as millions of corporate messages provide malicious actors with the means to compromise sensitive information, conduct unauthorized access, and potentially exploit confidential company resources.

“The leaked data could facilitate targeted attacks resulting in a full system takeover, corporate espionage, and other malicious activities, posing serious risks to the company’s security and integrity,” researchers warn.
The team believes that this type of leak is a goldmine for ransomware gangs. These groups often target victims who have the biggest potential to allow for supply-chain attacks, a type of intrusion that allows hitting the victim’s clients down the line.
“Since there are a multitude of parties involved and a vast amount of credentials shared, a successful hit on this database could result in a domino effect for all of their partners. One good example of such a scenario is the MOVEit attacks of 2023,” the team said.
We have reached out to Miracle Software but did not receive an official comment before publishing.
Miracle Software is a US-based systems integration company with over 2,600 employees under its wing. The company claims to serve 42 Fortune 100 companies and lists IBM, Google Cloud, Microsoft, AWS, and others as its partners.